
A player lost £1,375 in three minutes to a card he’d never owned, at a UK-licensed casino he trusted. The attack that did it never touched the casino’s defences, and it could just as easily target yours.
£1,375, gone in three minutes.
A long-standing Casinomeister forum member was watching the football when two emails hit his inbox. Between them, his online casino balance had been withdrawn to a Revolut card he’d never owned. He wasn’t actively using his account. He doesn’t even have a Revolut account. His report of what happened drew a long discussion.
This wasn’t a crypto casino or some dodgy offshore operator. It was a UK Gambling Commission–licensed site. If anything, one that this user had praised for years. Unfortunately, the casino’s first response was to tell him to file a police report and talk to his bank.
How is it my bank’s fault when the card used to steal my money isn’t theirs?
The affected player, on the Casinomeister forum
So How Do You Rob an Account the Owner Hasn’t Logged Into?
To help our community understand what happened here and avoid falling for the same scam, we’ve put that question to people who work inside the industry. The answer we keep getting is credential stuffing.
The process is pretty simple. An unrelated site you signed up to years ago gets breached, and your email, username and password leak. Those details get bundled into lists of stolen credentials, billions of them, traded openly.
The credentials aren’t hard to come by. One 2019 compilation known as “Collection #1,” which security researchers classified specifically as a set of credential-stuffing lists, held almost 2.7 billion email-and-password records covering 773 million unique addresses.
Attackers buy those lists and run automated scripts that fire the stolen email-and-password pairs at other sites, casinos included. Often the casino’s own login page helps them along. Enter an email that isn’t registered and many sites just tell you no account exists; enter one that is registered but get the password wrong, and the wording changes to something like “incorrect password.” Now the attacker knows the account is real, and can work through every leaked password tied to that email until one lets them in.
Accounts with money get emptied. Accounts with nothing get skipped, and the script moves to the next name on the list. It’s automated and it runs at scale, meaning many thousands of accounts tried within hours.
This works because people reuse passwords. It fits what happened to another user on the thread. His phone had already flagged that his casino password appeared in a known leak. Have I Been Pwned, the free service that catalogues this material, gives just two pieces of advice to anyone caught in it: change any reused password, and switch on two-factor authentication.
But that raises the obvious questions:
- Shouldn’t a UKGC-licensed casino block a withdrawal to a card in someone else’s name?
- Haven’t casinos brought in two-factor authentication by now?
Shouldn’t “Closed Loop” Have Stopped This?
UK-licensed casinos generally run a “closed loop” payment system which means that the money is meant to return to the source it came from, and you shouldn’t be able to fire a withdrawal at a random, unverified card.
But the “closed loop” assumes the person managing the account is its rightful owner. It governs where money is allowed to go. It doesn’t verify who is operating the account. And here is what makes this particular case so troubling.
This player had only ever used a single card on the account. Crucially, according to the player, there was no deposit from the Revolut card, no incoming payment that a closed loop could legitimately “return.” Just two withdrawals, three minutes apart, for £975 and £400.
That is exactly the scenario “closed loop” is supposed to make impossible. Its whole purpose is to ensure money can only be paid back to a verified source. So how does a brand-new, unverified card get added and drained in the space of three minutes?
The player put his finger on it:
There’s clearly something not right when a card can be added to an account without the account-holder’s knowledge, and then funds withdrawn to it, all in such a small window of time.
The affected player, speaking to Casinomeister
We don’t have the full answer, and we’re not going to speculate our way into publishing a blueprint. But at least one licensed operator we spoke to said it had already identified and closed the specific weakness that made this kind of theft possible, which rather suggests the gap exists.
Full disclosure: We were told how that fix works. We’re deliberately not publishing it. Casinomeister has been around since 1998 to help players and, in this case, spelling out the mechanics would do more to arm the next attacker than to protect a single player, and every defence a reader actually needs is further down this page.
Part of the problem lies in the payments system itself. Operators have no easy, reliable way to verify the name on a card.
As another source at a UK-licensed casino told us, there’s a separate API that lets operators confirm a card actually belongs to the account holder, but it’s new and, they said, still inaccurate. So while closed loop works, the mechanism to verify if a card belongs to the account holder is far weaker than most people assume.
Don’t UK Casinos Use Two-Factor Authentication?
The thread kept asking the obvious question: haven’t casinos brought in two-factor authentication by now? It’s the one control that would make a stolen password useless on its own. A second step, usually a rotating code, that an attacker with your login still can’t get past.
It is kind of ridiculous that in 2026 some (or many?) UK-licensed casinos still don’t offer 2FA at all, and plenty that do leave it optional and buried in account settings. So the players most at risk are likely the ones who never switch it on. Compare that to UK banking, where a second factor has been effectively mandatory for years under Strong Customer Authentication rules.
What Can the UKGC Do About This?
It would be unfair to say the British regulator ignores account security. The Gambling Commission’s technical standards already cover the systems that handle customer authentication and balances, and it expects licensed operators to protect players from “unnecessary security risks.”
That said, we believe the UKGC should make two-factor authentication mandatory. As things stand, the Commission encourages 2FA but does not require it, and it has generally preferred to set outcomes rather than dictate the exact technical measures operators must use. There’s a logic to that approach: prescriptive rules date quickly, and regulators want to avoid freezing the industry to yesterday’s technology.
But there’s an equally reasonable argument that account takeover is serious enough that some measures shouldn’t be optional. Banking regulators reached that conclusion years ago, but gambling accounts hold and move real money too.
The good news is that none of this requires reinventing the wheel. The tools already exist. Make 2FA mandatory and if you think players wouldn’t be happy, allow them to disable it should they choose to, making it clear that they’ll be exposed to a higher risk.
How to Avoid Getting Your Casino Account Robbed
No account anywhere is ever perfectly safe. Not your email, not your bank, not your casino. Some of the risk sits outside your control: a breach at some unrelated company, an operator’s own security gap, a leaked database you’ll never hear about. You can’t control those. But the specific attack in this story turns almost entirely on things you can control, and shutting it down takes about ten minutes. Start today:
- Create one unique, strong password per casino. If the password on your account exists nowhere else, a leak somewhere else can’t be stuffed into your account.
- Make your password long and hard to guess. Avoid real words, names, and predictable patterns; favour length and randomness.
- Check whether your casino offers 2FA, and turn it on if it does. Go into your account security settings and look: if it’s there, switch it on, and choose an authenticator app over SMS codes, which can be intercepted or SIM-swapped.
How This Case Ended
For the forum member who lost the £1,375, the story looks like it will end well enough. After the thread gathered attention, the operator came back to him. It said they have “investigated the matter and found no indication of any breach”, but that “as a gesture of goodwill, we will cover the losses you incurred due to the fraud.” And it confirmed something telling:
We are also adding the option to enable two-factor authentication (2FA), which will provide an additional layer of security for customer accounts. Will become available soon.
The operator, responding on the Casinomeister forum
It’s interesting, to say the least, how there was no break-in at the casino, and yet the money was gone, and the fix now being rolled out is the exact control that was missing all along: a second factor.
The player felt the same way, describing the stress of changing passwords and freezing bank accounts in the days that followed.
The addition of 2FA can’t come soon enough
The affected player, speaking to Casinomeister
This player will get his money back. The next one might not be so lucky, and probably won’t have a forum full of people pushing on their behalf.
If it does happen to you, don’t accept “go and talk to your bank” as the end of it. Instead:
- Freeze the affected cards
- Change your passwords
- Put your complaint in writing to the operator and the regulator
If they brush you off, you don’t have to fight it alone. Casinomeister runs a free player complaint service that has helped players recover money from licensed operators for years.
The player who lost that money could have kept quiet, taken his refund, and moved on. Instead he let us tell his story, because he wanted others to see it coming.
We all need to be more security-conscious in these times,” he told us, “so the more awareness the better, whether it’s players, customers or businesses.
The affected player, speaking to Casinomeister
Latest Blog Articles
One of the things you need to remember when you’re playing at online casinos is that casinos are businesses; they’re there to make money, and the w…
Boxers can earn insane amounts of money – everyone knows that. However, due to the dangerous nature of the sport and the limited fitness period in …
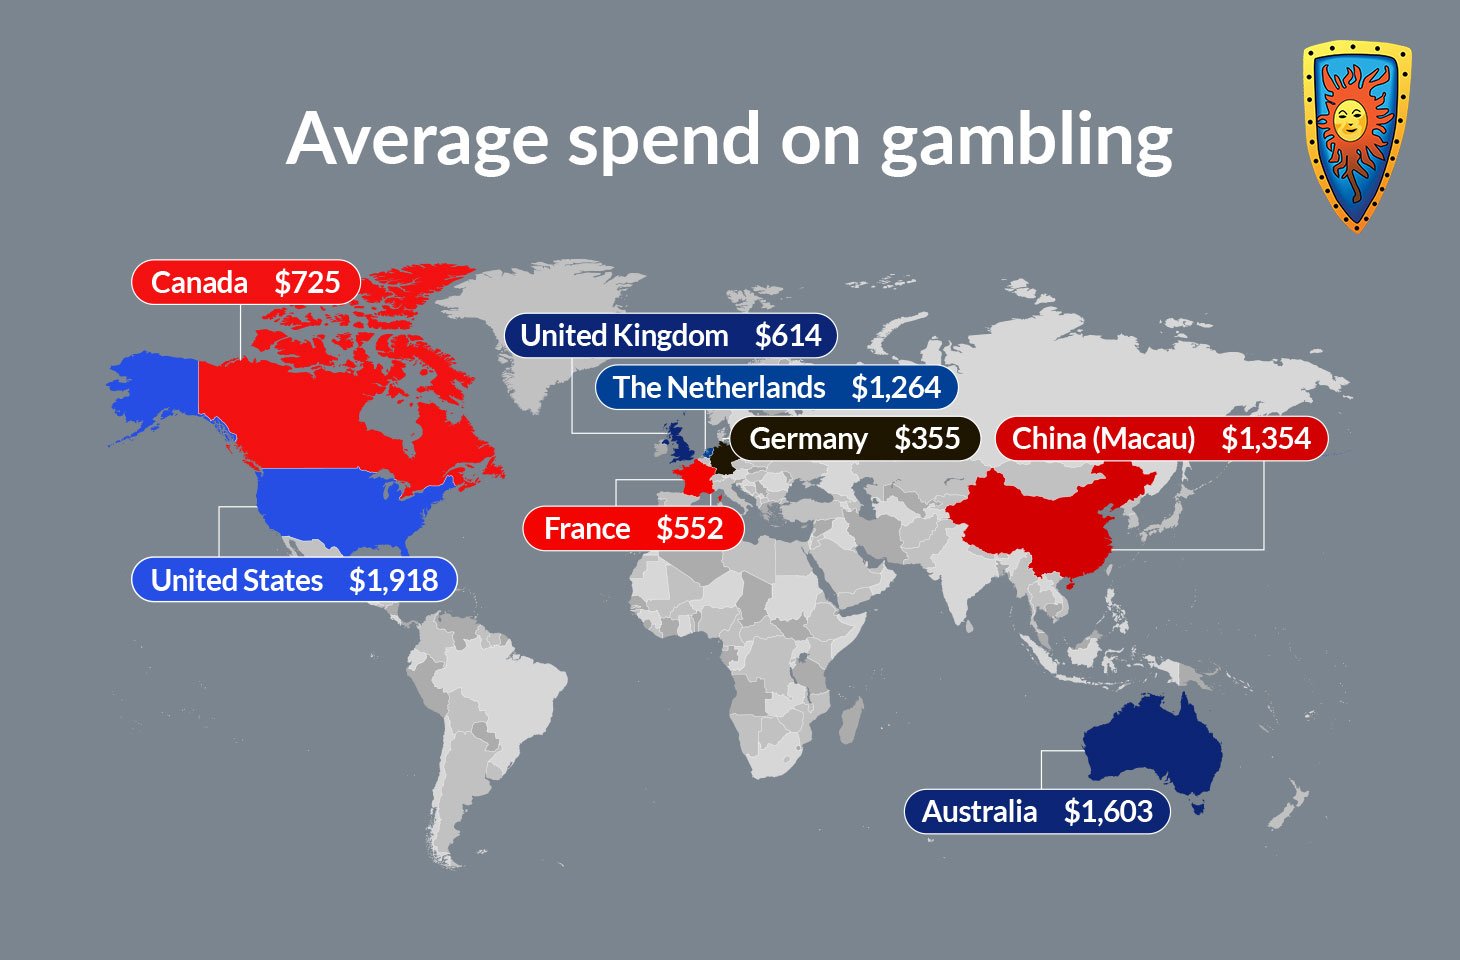
Key highlights: Not every player in the world gambles through the roof, but the ones who do probably live in Macau, Australia, the Netherlands, t…